Modifying the Windows 7 boot loader with the Boot Configuration Data Editor tool

In Windows Vista and later versions of Windows, the bootloader was moved from boot.ini to a utility called BCDEdit. Here’s how to modify the boot config data with the new tool.

Sometimes dual-booting a system is a handy way to test new software, a new operating system, or an application that needs to be run in a specific version of Windows. Other reasons to dual-boot might include replication of a client environment.

Windows handles dual-booting by using boot.ini to display a menu of bootable choices or partitions found on the current system. In Windows Vista and later versions of Windows, the bootloader was moved from boot.ini to a utility called BCDEdit.

Recently, we decided we could make better use of some disk space that we had set aside to create a bootable VHD for Windows Server 2008 R2. There was no data other than the OS installation contained within the file because we had used it only to prepare a blog post about booting from Virtual Hard Disks. To free up the space, we deleted the VHD.

Note: Always make sure to back up any data that you want to keep before deleting or modifying partitions on VHDs. Your changes could make the partition unbootable.

Once we had the VHD removed, we thought Windows would be smart enough to clean up the boot loader, but we were not so lucky. We had Windows 7 set as the primary OS, so we were not without a system.

We started looking around for boot.ini and was directed toward the Boot Configuration Data Editor (BCDEdit) as the utility to use when editing boot loader information in Windows 7 (and in Vista too).

To begin, open the Start menu, select All Programs, and then choose Accessories. Right-click on Command Prompt and select Run As Administrator. Once in the command window, type bcdedit. This will return the current running configuration of your boot loader, showing any and all items that can boot on this system.

In this example, we decided to remove the entry for my Windows 2008 R2 installation, as we wouldn’t need it for the time being. To remove an entry, you will need to know the Boot Loader Identifier (found in curly braces in Figure A).

Figure A

we copied the whole list into Notepad and then selected and copied just the ID, braces included.

Removing an entry from the Boot Loader

One simple command got the Windows Server 2008 R2 entry out of the boot loader. At the command prompt, enter the following:

Bcdedit /delete {boot loader identifier}

Press Enter, and the Boot Configuration Data Editor (BCDEdit) will remove the entry for the ID you specified and display a message when finished. When Windows starts, the only choice available in the boot menu should be the current Windows installation.

Warning: Be careful when editing the boot configuration data. If you mistakenly remove the current instance of Windows, you may render your computer unbootable.

Have questions?

Get answers from Microsofts Cloud Solutions Partner!
Call us at: 856-745-9990 or visit: https://southjerseytechies.net/

South Jersey Techies, LL C is a full Managed Web and Technology Services Company providing IT Services, Website Design Services, Server Support, Network Consulting, Internet Phones, Cloud Solutions Provider and much more. Contact for More Information.

To read this article in its entirety click here.

Old Windows PCs can stop WannaCry ransomware with new Microsoft patch

In a rare step, Microsoft published a patch for Windows XP, Windows Server 2003 and Windows 8


Users of old Windows systems can now download a patch to protect them from this week’s massive ransomware attack.

In a rare step, Microsoft published a patch for Windows XP, Windows Server 2003 and Windows 8 — all of them operating systems for which it no longer provides mainstream support.

Users can download and find more information about the patches in Microsoft’s blog post about Friday’s attack from the WannaCry ransomware.

The ransomware, which has spread globally, has been infecting computers by exploiting a Windows vulnerability involving the Server Message Block protocol, a file-sharing feature.

Computers infected with WannaCry will have their data encrypted, and display a ransom note demanding $300 or $600 in bitcoin to free the files.

Fortunately, Windows 10 customers were not targeted in Friday’s attack. In March, Microsoft patched the vulnerability that the ransomware exploits — but only for newer Windows systems. That’s left older Windows machines, or those users who failed to patch newer machines, vulnerable to Friday’s attack.

Researchers originally believed the ransomware was spread through attachments in email phishing campaigns. That no longer appears to be the case.


Infection attempts from the WannaCry ransomware.

Once a vulnerable PC becomes infected, the computer will attempt to spread to other machines over the local network as well as over the internet. The ransomware will specifically scan for unpatched machines that have the Server Message Block vulnerability exposed.

Businesses can prevent this by disabling the Server Message Block protocol in vulnerable PCs. They can also use a firewall to block unrecognized internet traffic from accessing the networking ports the Server Message Block uses.

Fortunately, Friday’s ransomware attack may have been contained. A security researcher who goes by the name MalwareTech has activated a sort of kill-switch in WannaCry that stops it from spreading.

As a result, over 100,000 new infections were prevented, according to U.K.’s National Cyber Security Centre. But experts also warn that WannaCry’s developers may be working on other versions that won’t be easy to disable.

“It’s very important everyone understands that all they (the hackers) need to do is change some code and start again. Patch your systems now!” MalwareTech tweeted.

Unfortunately, the kill-switch’s activation will provide no relief to existing victims. The ransomware will persist on systems already infected.

Friday’s ransomware attack appears to have spread mainly in Europe and Asia, with Russia among those nations hardest hit, according to security researchers.

Security experts are advising victims to wait before paying the ransom. It’s possible that researchers will develop a free solution that can remove the infection.

Have questions?

Get answers from Microsofts Cloud Solutions Partner!
Call us at: 856-745-9990 or visit: https://southjerseytechies.net/

South Jersey Techies, LL C is a full Managed Web and Technology Services Company providing IT Services, Website Design Services, Server Support, Network Consulting, Internet Phones, Cloud Solutions Provider and much more. Contact for More Information.

To read this article in its entirety click here.

What you need to know about the WannaCry Ransomware

What has happened?

On May 12, 2017 a new variant of the Ransom.CryptXXX ransomware family (detected as Ransom.Wannacry) began spreading widely, impacting a large number of organizations, particularly in Europe.

What is the WannaCry ransomware?

WannaCry encrypts data files and asks users to pay a US$300 ransom in bitcoins. The ransom note indicates that the payment amount will be doubled after three days. If payment is not made after seven days, the encrypted files will be deleted.

Figure 1. Ransom demand screen displayed by the WannaCry Trojan

It also drops a file named !Please Read Me!.txt which contains the ransom note.

Figure 2. Ransom demand note from WannaCry Trojan

It propagates to other computers by exploiting a known SMB remote code execution vulnerability (MS17-010) in Microsoft Windows computers.

Are you protected against this threat?

South Jersey Techies, LLC recommends and offers Symantec Endpoint Protection to its clients. Symantec Endpoint Protection customers are protected against WannaCry using a combination of technologies: Antivirus, SONAR protection, Network-based protection.

All South Jersey Techies Managed IT Services client computers have the latest Windows security updates installed, in particular MS17-010, to prevent spreading. If your business / organization is not on our Managed IT Services plan please check or contact us to ensure that you have the latest updates installed.

Who is impacted?

A number of organizations globally have been affected, the majority of which are in Europe.

Is this a targeted attack?

No, this is not believed to be a targeted attack at this time. Ransomware campaigns are typically indiscriminate.

Can I recover the encrypted files?

Decryption is not available at this time but companies are investigating. South Jersey Techies, LLC does not recommend paying the ransom. Encrypted files should be restored from back-ups where possible. South Jersey Techies offers a number of backup solutions including Carbonite Online Backup and cloud storage solutions. If you are unsure about your computer / server backups, please check or contact us to discuss the best solution for your business.

What are best practices for protecting against ransomware?

  • New ransomware variants appear on a regular basis. Always keep your security software up to date to protect yourself against them.
  • Keep your operating system and other software updated. Software updates will frequently include patches for newly discovered security vulnerabilities that could be exploited by ransomware attackers.
  • Email is one of the main infection methods. Be wary of unexpected emails especially if they contain links and/or attachments.
  • Be extremely wary of any Microsoft Office email attachment that advises you to enable macros to view its content. Unless you are absolutely sure that this is a genuine email from a trusted source, do not enable macros and instead immediately delete the email.
  • Backing up important data is the single most effective way of combating ransomware infection. Attackers have leverage over their victims by encrypting valuable files and leaving them inaccessible. If the victim has backup copies, they can restore their files once the infection has been cleaned up. However organizations should ensure that back-ups are appropriately protected or stored off-line so that attackers can’t delete them.
  • Using cloud services could help mitigate ransomware infection, since many retain previous versions of files, allowing you to “roll back” to the unencrypted form.

Have additional questions?

Feel free to call us at contact us or (856) 745-9990 with any questions you may have.

Quick Tips: Flush the ARP cache in Windows 7

Here’s how to clear the Address Resolution Protocol cache and how to manage that cache with a few command switches.
The Address Resolution Protocol (ARP) cache is a crucial component of IP networking on any operating system. What ARP does is link Ethernet addressing (IP addressing) to hardware addressing (MAC addressing). Without this system, a machine could not communicate to the outside world as one addressing scheme could not communicate with the other.

The ARP Cache is a collection of ARP entries (mostly dynamic) that are created when a hostname is resolved to an IP address and then an IP address is resolved to a MAC address (so the computer can effectively communicate with the IP address).

When this happens, the PC will store that newly mapped address in the ARP cache, and it will stay there until the ARP cache entry timeout expires. This isn’t usually a problem, but sometimes a bad ARP entry can cause issues with Internet connections and Web page loading. When this occurs, one step that can be taken toward resolution is to clear the ARP cache. Yes, this means the ARP cache has to be rebuilt, which means a little more work for the PC, but that cache will rebuild fairly quickly.

Clearing the ARP cache is done completely through the command line, so stretch out those fingers and get ready to type. After we show you how to clear the ARP cache, we will show you how to manage that cache with a few command switches.

Flush the cache

Step 1: Open the command prompt

Click Start and then type “cmd” (no quotes) in the search dialog box, but don’t hit Enter yet. Right-click the cmd.exe icon and select Run as Administrator (Figure A). After answering the UAC, the terminal window will open offering up the command prompt.

Figure A
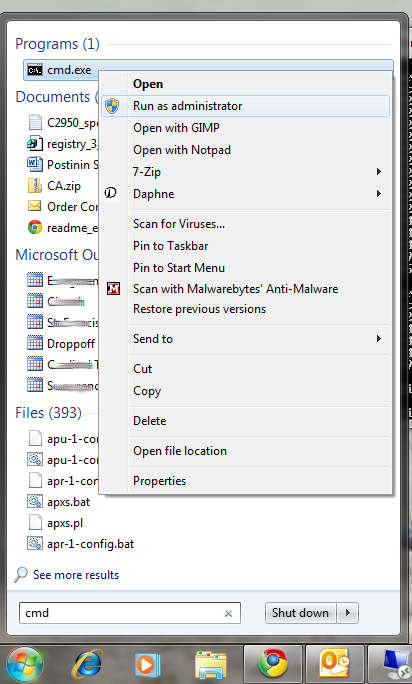
If the icon is already pinned in the Start menu, entering cmd is not necessary.

Step 2: Run the commands

The first command to run is

arp -a

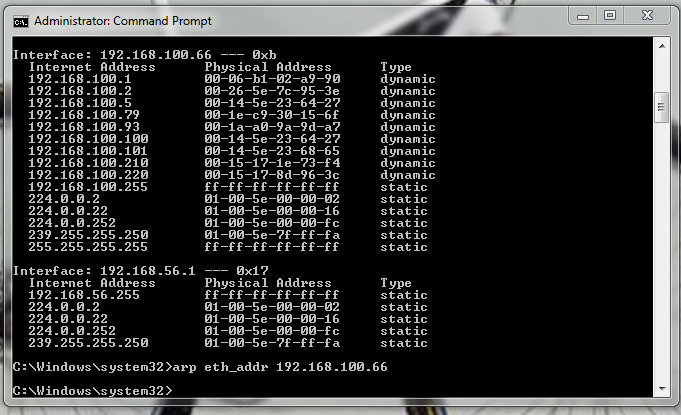
This command will display all your ARP entries (Figure B). Naturally the -a option is not the only option available. The arp command also allows for the following switches:

-d Delete an IP address (arp -d 192.168.100.10)
-d -a Delete all entries in the ARP table
-s Add an entry to the ARP table (arp -s ADDRESS MAC_ADDRESS – Where ADDRESS is the address to be added and MAC_ADDRESS is the MAC address of the machine)

Figure B

Here you see the arp cache for two different interfaces on a single machine.

To flush the entire cache, issue the following command:

netsh interface ip delete arpcache

The above command will flush the entire ARP cache on your system. Now as soon as network connections are made, the ARP cache will begin to repopulate.

Verify the flush

Once you have flushed the ARP cache, make sure to issue the command arp -a to see if the cache has, in fact, been flushed. If it does not flush, it could be the system is a victim of a Windows bug caused when Routing and Remote Services is enabled. This is a simple bug to fix:

1.           Click Start | Control Panel.

2.           Click Administrative Tools.

3.           Click Computer Management.

4.           Double-click Services and Applications.

5.           Double-click Services.

6.           Scroll down to Routing and Remote Services.

7.           Double-click Routing and Remote Services.

8.           Set the Startup Type to Disable.

9.           Make sure the service is stopped.

Now try flushing the ARP cache again. It should work this time.

Troubleshooting

It is also possible to troubleshoot network connections using the ARP cache. For example, it is important to look out for invalid ARP entries that go to a MAC address of 00-00-00-00-00-00. If one such entry shows up, make sure to delete it from the cache using the -d switch. Say you have an ARP entry that looks like:

224.0.0.24           00-00-00-00-00-00 static

In order to delete this entry, use the arp command like so:

arp -d 224.0.0.24

And that invalid entry will be gone.

Final thoughts

There are so many ways to troubleshoot networking connections. Flushing the ARP cache is just one of those methods that is rarely thought of, but when all else fails this might be the last-gasp effort that makes you the hero of the day.

Have questions?

Get answers from Microsofts Cloud Solutions Partner!
Call us at: 856-745-9990 or visit: https://southjerseytechies.net/

South Jersey Techies, LL C is a full Managed Web and Technology Services Company providing IT Services, Website Design Services, Server Support, Network Consulting, Internet Phones, Cloud Solutions Provider and much more. Contact for More Information.

To read this article in its entirety click here.

Microsoft teases Windows 10’s sleek new look for the future

“Project Neon” will give your Windows 10 PC a fresh coat of paint later in 2017.

Microsoft’s planning a sleek visual refresh for Windows 10, and the company quietly teased its first official glimpse of what’s coming in the future during the Windows Developer Day keynote on Wednesday.

There aren’t many details being shared about “Project Neon” right now—as the refresh was called in earlier leaks—but the new visual look will focus on animations and transitions. The basic concept is “to add fluidity, animation, and blur to apps and the operating system,” as first reported by Windows Central. The new design language also hopes to make it easier for developers to create attractive apps.

The design refresh should extend to all Windows 10 devices including PCs and tablets, HoloLens, Xbox, and the few surviving Windows Phones, according to Windows Central.

Twitter user Tom Hounsell shared a clean version of Microsoft’s first look at Windows 10’s forthcoming design tweaks. The image shown on the livestream had large text overlaid on top of the screenshot.

As you can see, this isn’t a huge change, but the visual refresh gives Windows 10 a sleeker, more modern feel. The taskbar icons look a little more dynamic and bolder. Cortana is using the icon instead of the search box, though it’s not clear if this will be the default look. The clock on the taskbar is also bolder, and the usual notification area icons including the Action Center are notably absent. The open Groove Music window itself looks more polished and Aero-esque as well, with no title bar to be seen—just unobtrusive options in the app’s upper-right corner.

The impact on you at home: Windows Central says that some of the code for Project Neon is already available in recent Insider Preview builds of Windows 10; however, it’s unlikely the visual refresh will be ready in time for the massive Creators Update this spring. Microsoft is expected to share more information about Neon during the Build conference in May. The Creators Update is expected to roll out in late March or early April, followed by a second major update later in 2017.

Have questions?

Get answers from Microsofts Cloud Solutions Partner!
Call us at: 856-745-9990 or visit: https://southjerseytechies.net/

South Jersey Techies, LL C is a full Managed Web and Technology Services Company providing IT Services, Website Design Services, Server Support, Network Consulting, Internet Phones, Cloud Solutions Provider and much more. Contact for More Information.

To read this article in its entirety click here.

Windows Tip of the week: How to turn hibernation on and off

How to turn hibernation on and off:

When your PC goes to sleep, it enters a low-power state, ready to spring back into action when Windows detects a tap on the keyboard or determines that it’s time to run a scheduled task. If you’re planning to be away from the PC for a while, you might prefer to save the current state so that you can restore it quickly, without the chance that the computer will wake up on its own.

There’s an option that lets you save the contents of memory to a hibernation file and then shuts down the PC, so it uses no power at all. When you restart, Windows restores the system state from the hibernation file.

To enable or disable hibernation, open a Command Prompt window and enter the powercfg command with the -h switch. Type powercfg -h on to enable hibernation; substitute the word off to disable it.

Normally, the Hibernate option is hidden from the Shutdown menu. To make it visible, open Power Options in Control Panel and then click Choose What The Power Buttons Do. Under the Shutdown Settings heading, select the Hibernate checkbox to display it in the Power menu.

Have questions?

For More Tips & Info from Microsofts Cloud Solutions Partner!
Call us at: 856-745-9990 or visit: https://southjerseytechies.net/

South Jersey Techies, LL C is a full Managed Web and Technology Services Company providing IT Services, Website Design Services, Server Support, Network Consulting, Internet Phones, Cloud Solutions Provider and much more. Contact for More Information.

CALL US NOW!